
Rust in the Linux Kernel: A Beacon Against AI-Driven Bugs
Rust in the Linux Kernel: A Beacon Against AI-Driven Bugs Quick Verdict Greg Kroah-Hartman's assertion that "Rust will save Linux from AI" is a compelling argument rooted in practical security needs. While not a magic

Rust in the Linux Kernel: A Beacon Against AI-Driven Bugs
Quick Verdict
Greg Kroah-Hartman's assertion that "Rust will save Linux from AI" is a compelling argument rooted in practical security needs. While not a magic bullet, Rust's unique strengths in memory safety and concurrency are already proving invaluable in tackling a surge of AI-discovered vulnerabilities, making it a critical, evolutionary step for the kernel's future stability and security.
The Challenge: Linux Under AI's Scrutiny
The Linux kernel, a bedrock of modern computing, is facing an unprecedented security challenge. According to Greg Kroah-Hartman, a prominent Linux stable kernel maintainer, the advent of sophisticated AI bug-detection programs has led to a "flood of serious Linux security holes being discovered." This includes notable vulnerabilities like Dirty Frag, Copy Fail, and Fragnesia. Kroah-Hartman, who has observed kernel security bugs since 2005, notes the kernel team is now issuing an astonishing "13 CVEs [Common Vulnerabilities and Exposures] a day, or something, something crazy." This rapid rate of discovery highlights a fundamental weakness in the traditional C language, where the majority of these bugs originate.
C's long-standing pitfalls, such as dereferencing pointers without checks, forgotten locks, and unreleased memory leaks, are precisely the "tiny, minor stuff" that accumulate over time, leading to kernel crashes and vulnerabilities. Kroah-Hartman emphasizes, "This is what we live with in C. This is why we don't like it." The sheer volume of code (36 million lines in C) combined with the human-intensive nature of code review makes catching these subtle errors a Herculean task for the approximately 700 kernel maintainers overseeing 5,000+ developers.
Rust's Role: Compiler-Enforced Security and Simplified Review
Rust emerges as a pivotal solution to these deep-seated issues. Its primary advantage, as Kroah-Hartman highlights, is its ability to catch these common C mistakes at "build time, not review time." This pre-emptive error detection is a game-changer. For instance, Rust's locking abstractions ensure that access to critical data structures is only granted once a lock is obtained, and the lock is automatically released. The compiler simply "will not let you" write code that violates these safety guarantees. This mechanism directly addresses a huge fraction of the bugs seen in C, potentially eliminating "60% of the bugs in the kernel right there, they're gone."
This shift significantly alleviates the burden on human maintainers. Instead of scrutinizing every line for proper error checks and lock management, maintainers can trust the compiler to enforce these fundamental invariants. This allows them to "focus on the logic" and review code more efficiently. The outcome is simpler coding and a reduction in bugs, as patterns that ensure correctness become obvious and enforceable.
Beyond its direct application, Rust has had a profound indirect influence on the C codebase. Kroah-Hartman acknowledges that the kernel community "stole this from Rust" by adopting concepts like scoped locks and allocators, which make C code harder to get wrong and simpler to write. The Rust-for-Linux team has also pushed for changes in C interfaces, simplifying driver development and making them "harder to write [wrong]."
Perhaps the most ambitious aspect of Rust's integration is the push for handling "untrusted data." By introducing an "untrusted" type wrapper and a validate method, Rust forces explicit validation when data crosses from untrusted sources (like user space or even malicious hardware) to trusted kernel space. This design concentrates the validation logic, making it easier to review and, according to Kroah-Hartman, could eliminate "80% of all the CVEs we have."
Implementation: Evolutionary, Not Revolutionary
It's crucial to understand that Rust is not presented as a "silver bullet." Kroah-Hartman readily admits that Rust code can still have bugs, citing an early Rust component that had a memory flaw due to unchecked buffer size. The vision for Rust integration is evolutionary, not a full rewrite of the 36 million lines of existing C code.
Instead, the focus is on new development. Subsystems are already mandating new drivers, such as for graphics, be written in Rust. Over the next one to two years, a significant shift is expected, with new hardware support leaning heavily towards Rust. The strategy involves letting new Rust drivers gradually replace old C drivers as hardware evolves, with the expectation that old code will eventually be deleted "after about 20 years."
The "Rust experiment is over" for the Linux kernel maintainers; it's now considered a permanent and integral part of the kernel's future. The commitment of the Rust-for-Linux team and the demonstrated benefits have solidified its position. A practical example of this commitment is Android's Binder, its core interprocess communication mechanism. Both C and Rust implementations are coexisting temporarily, with the C version expected to be removed once the Rust version reaches parity. This means that soon, "billions of devices" will be running Rust code within the Linux kernel.
Pros and Cons
Pros:
- Enhanced Security: Significantly reduces entire classes of C-related bugs (memory safety, concurrency issues) by enforcing checks at build time.
- Simplified Code Review: Frees up maintainers to focus on logic rather than resource management, optimizing the review process.
- Improved C Code: Rust's influence has led to cleaner, safer patterns being adopted in C development within the kernel.
- Proactive Vulnerability Mitigation: The untrusted data model focuses validation efforts, potentially eliminating a vast majority of CVEs.
- Future-Proofing: Positions Linux to better withstand the increasing threat of AI-driven bug discovery.
- Gradual, Sustainable Adoption: Evolutionary approach prevents disruption of the massive existing codebase.
Cons:
- Not a Panacea: Rust is not immune to all bugs; logical errors can still occur.
- Legacy Code Burden: The vast existing C codebase means full benefits will only be realized over a long period as new Rust code replaces old C components.
- Binding Overhead: Initial effort required to create bindings for Rust to interact with existing C components, sometimes leading to a "chicken-and-egg" problem.
- Learning Curve: Requires developers to adopt a new language and its paradigms.
Recommendation
Kroah-Hartman's vision for Rust in the Linux kernel is not just a theoretical discussion; it's a strategic imperative. For anyone invested in the long-term stability and security of Linux, this development is unequivocally positive. The decision by kernel maintainers to move past the "experiment" phase and embrace Rust full speed ahead signals a confident step towards a more robust, secure operating system. While the transition will be gradual, the immediate and long-term benefits in terms of bug reduction and maintainer efficiency are too significant to ignore. Rust is poised to play a crucial role in safeguarding Linux against the advanced analytical capabilities of AI.
FAQ
Q: Will the entire Linux kernel be rewritten in Rust? A: No, the plan is not to rewrite the existing C codebase. Instead, new components, drivers, and subsystems will increasingly be written in Rust, gradually replacing older C code over time as hardware and requirements evolve. The focus is on new development.
Q: How does Rust specifically address the security issues found by AI? A: Rust's compiler-enforced memory safety and robust type system prevent common C errors like null pointer dereferences, data races, and memory leaks at build time. This eliminates a large class of vulnerabilities that AI bug detectors are currently adept at finding, making the resulting code inherently more secure.
Q: When can users expect to see the benefits of Rust in Linux? A: Users are already beginning to see benefits, particularly through ongoing improvements in C code influenced by Rust. More direct impacts, such as enhanced security from Rust-written drivers and components, are expected to become prevalent over the next year or two, with significant deployments like Android's Binder already underway for billions of devices.
Related articles
Android 17 QPR2 Beta 7.1: The Performance Relief You've Been Waiting
Android 17 QPR2 Beta 7.1: Finally Fixing the QPR1 Performance Woes Verdict: Android 17 QPR2 Beta 7.1 is a crucial and highly anticipated software update for Google Pixel users, specifically targeting and resolving the

DJI Solo Video Setups: Smart Choices for Lone Creators
This review delves into DJI's recommended solo video setups, highlighting the Osmo Pocket 3 Creator Combo as a top pick for its integrated camera, gimbal, and mic. It also covers stabilizers like the Osmo Mobile 8 and RS 4, and the DJI Mic Mini series for enhanced audio, providing honest pros, cons, and clear buying advice.
Ars Technica's Rocket Report: Your Essential Space Industry Briefing
Quick Verdict Ars Technica's Rocket Report, presented by veteran space reporter Stephen Clark, offers an invaluable and meticulously organized weekly (or similar frequency, implied by "Edition 9.15") digest of the most
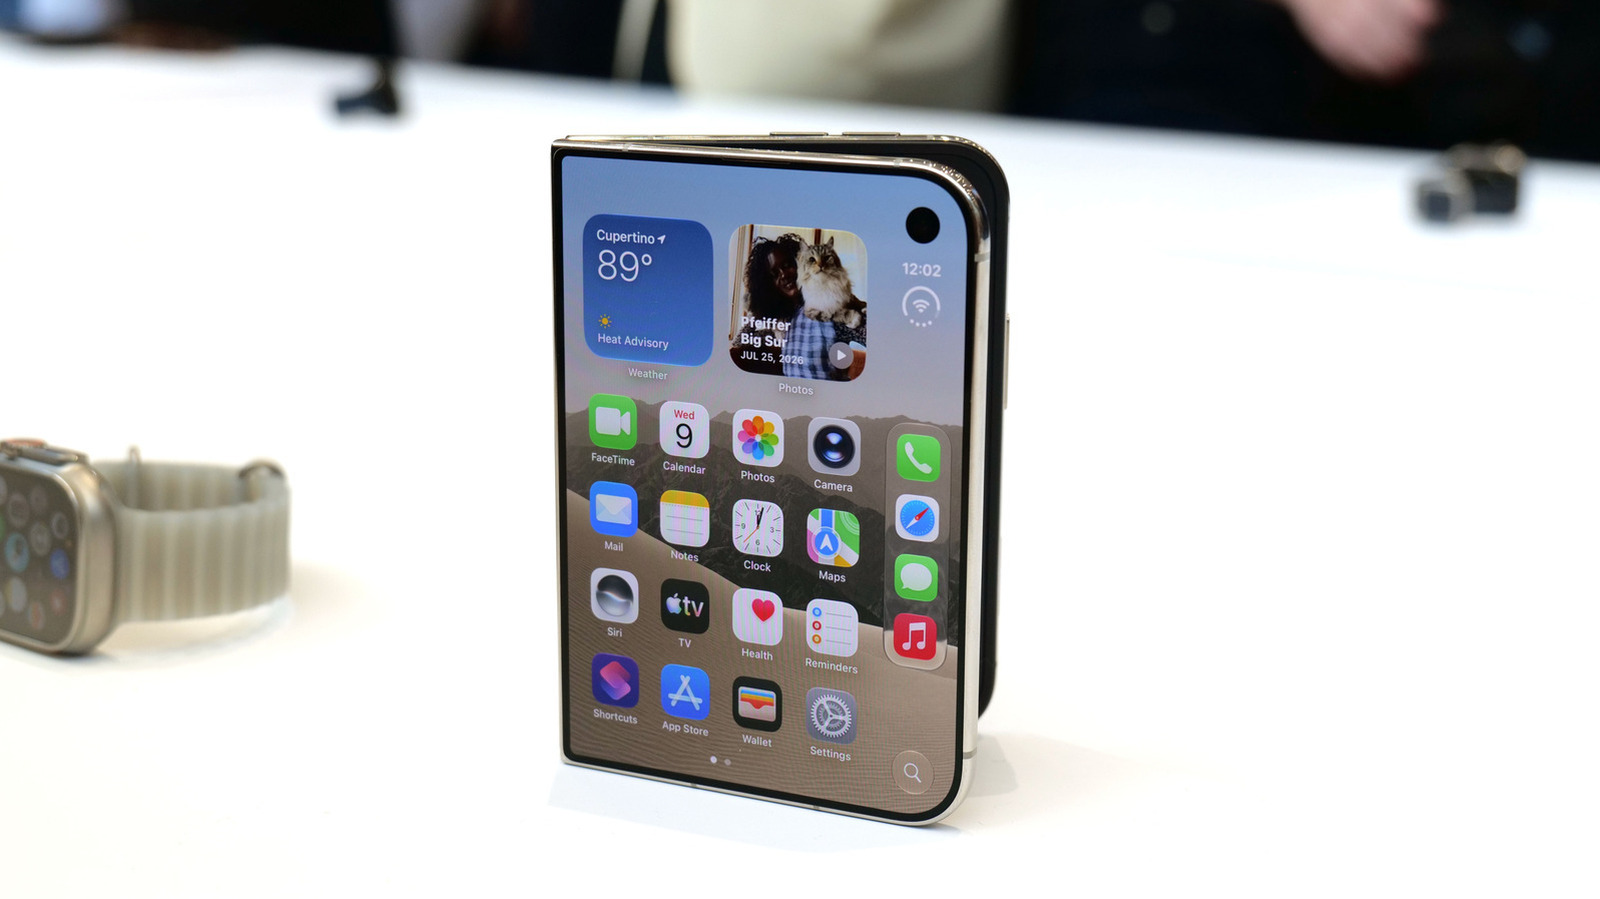
Apple iPhone Duo: A Daring Debut with Notable Compromises
Apple's highly anticipated iPhone Duo, priced at $2,000, has gone on pre-order. While hailed as "Apple's most exciting device in a decade" for its innovative foldable design and immersive display, it comes with significant drawbacks like the absence of FaceID and a premium camera.
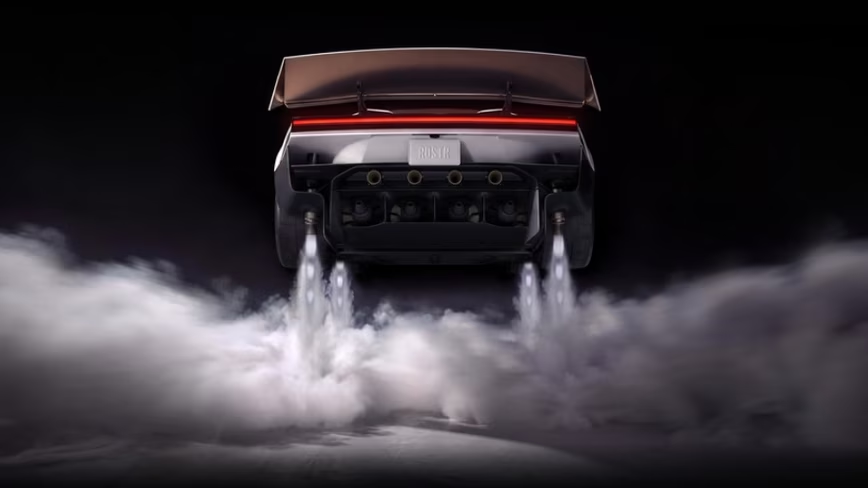
Tesla Unveils Thruster-Equipped Roadster, 2028 Production Targeted
Tesla has unveiled its second-generation Roadster, featuring cold-gas thrusters co-developed with SpaceX, enabling it to jump and flip. The electric sports car demonstrated 0-60mph in an astonishing 0.81 seconds, with production targeted for 2028. This highly anticipated reveal also serves as a key recruitment tool for Tesla's ambitious AI and robotics initiatives.

AI's Confidence vs. Formal Methods' Rigor: Design Flaws & Verification
While AI accelerates code generation, formal methods remain critical for ensuring system correctness. Languages like TLA+ and tools like Quint enable developers to model and verify system designs before coding, catching subtle flaws. Quint makes formal methods more accessible with developer-friendly syntax and executability. This approach is vital for verifying AI-generated code through trace validation and model-based testing, ensuring reliability against real-world data.