Passkeys: A Developer's Perspective on Their Current Limitations
For the past few years, the tech industry, particularly major players like Google and Microsoft, has aggressively promoted passkeys as the ultimate solution for logging in. They often present passkeys as an easier, more
For the past few years, the tech industry, particularly major players like Google and Microsoft, has aggressively promoted passkeys as the ultimate solution for logging in. They often present passkeys as an easier, more effortless alternative, sometimes requiring users to dig through settings to opt out of the prompt. Google even labels its setting “Skip password when possible,” while Microsoft advocates for entirely passwordless accounts.
Technologically, passkeys are undeniably impressive. Their fundamental design, being bound to the specific site they're created for, makes them inherently resistant to phishing attacks from fake login screens. Furthermore, their asymmetric nature means that even if a service experiences a data breach, the passkeys themselves cannot be recovered from server-side details. These robust security properties make passkeys an excellent fit for high-security corporate environments.
The Double-Edged Sword of Passkeys for Personal Use
Despite their technical advantages against man-in-the-middle attacks, passkeys present a different set of risks for individual users. For personal security, the primary concerns often revolve around permanent account lockout, automated account bans, and the loss of devices. While passkeys enhance security against phishing, they can paradoxically increase the probability of losing access to accounts under these common scenarios.
This creates a false sense of security. An account's overall resilience remains dependent on its weakest recovery method, whether that's SMS, email links, or security questions. If these standard recovery options are not adequately secured or enabled, the risk of permanent lockout for a user reliant on passkeys remains substantial.
Hardware Keys: The Cost of Security
When it comes to hardware keys, passkey management introduces several practical limitations. Unlike passwords, passkeys cannot simply be backed up or moved between hardware keys. Instead, users are typically required to enroll 2-3 separate hardware keys for every site they wish to secure. This quickly becomes expensive and unscalable as an individual's number of online accounts grows.
Many websites are increasingly adopting discoverable credentials, which allow the site to query the hardware key for a username instead of requiring the user to type it. While convenient, discoverable credentials on hardware keys have inherent limits, typically supporting between 25 and 100 accounts, with high-end keys managing up to 300. Exceeding this limit necessitates either deleting existing accounts from the key or purchasing additional sets of hardware keys, further escalating costs and complexity.
The Walled Garden of Synced Passkeys
Both Apple and Google actively encourage users to anchor their digital identity to their respective operating systems by using their synced passkey management systems. This “happy path” tightly integrates passkeys with the user's Apple or Google account. However, this convenience comes with a significant risk: if Google or Apple's automated systems decide to ban a user's account—a situation that has happened, sometimes controversially—the user could irreversibly lose access to all passkeys linked to that account across all third-party services.
The FIDO Alliance is working towards improving interoperability and simplifying passkey export, but the current experience remains fragmented and inconsistent across different providers. While future improvements are anticipated, the ecosystem is not yet mature enough to depend on for easy portability. This stands in stark contrast to a password, which is fundamentally just a string that can be easily exported and managed by hand if needed.
Third-Party Managers: A Glimmer of Hope, Not Yet Reality
For users accustomed to storing credentials in third-party password managers like Bitwarden or KeePassXC, integrating passkeys can be challenging. Despite recent efforts by operating systems to introduce APIs, such as Android's Credential Manager, that allow third-party tools to hook into passkey management, the user experience is still fragmented. It lacks the decades of UI/UX refinement that password autofill has achieved, particularly remaining inconsistent for autofill outside of web browsers and within native applications. While third-party passkey management is likely the future, it is not yet a seamless or reliable solution today.
Navigating Multi-Device Logins
Passkeys shine when logging into accounts on personally owned devices. However, their convenience significantly diminishes when dealing with shared or unfamiliar computers, such as a colleague's machine. Options include plugging in a hardware key, which isn't always feasible due to port availability or policy restrictions. Alternatively, signing in with a synced passkey risks exposing all other synced credentials to an untrusted device. The “Hybrid Transport” method, which involves scanning a QR code and connecting via Bluetooth to the computer, offers a secure theoretical solution but is often plagued by real-world issues like connection failures or unsupported Bluetooth functionalities.
Are Passkeys Ready for Everyone?
In conclusion, while passkeys offer compelling security benefits for enterprise users, the current ecosystem is not yet mature enough for the average individual. The day-to-day risks of account recovery and permanent lockout associated with passkeys often outweigh the benefits of enhanced protection against sophisticated AiTM proxy phishing attacks, especially when compared to the known phishing vulnerabilities of TOTP codes.
For most users, a combination of strong, randomly generated passwords stored in a reputable third-party password manager, paired with an independent TOTP app, still offers superior control and flexibility without sacrificing security. This approach empowers the user rather than ceding control to platform providers. Passkeys represent a significant security upgrade for individuals who previously reused passwords across multiple sites. However, for those already employing good password hygiene and multi-factor authentication, the current passkey experience can feel like a step backward.
FAQ
Q: What makes passkeys resistant to phishing? A: Passkeys are cryptographically bound to the specific site they are created for. This means they cannot be tricked into authenticating with a fake login screen, making them inherently resistant to traditional phishing attacks where users are lured to fraudulent websites.
Q: Why are hardware keys problematic for passkey backup and scaling? A: Passkeys cannot be backed up or moved between hardware keys; instead, each hardware key must be individually enrolled for every site. Additionally, hardware keys supporting discoverable credentials have limited storage, typically 25-100 accounts (up to 300 for high-end keys), requiring users to purchase more keys or delete accounts once capacity is reached.
Q: What is the primary risk associated with using platform-synced passkeys (e.g., Apple or Google)? A: The primary risk is permanent account lockout. If the platform provider (Apple or Google) bans or disables the user's account for any reason, the user could irreversibly lose access to all passkeys synced through that account, thereby losing access to all associated third-party services as well.
Related articles
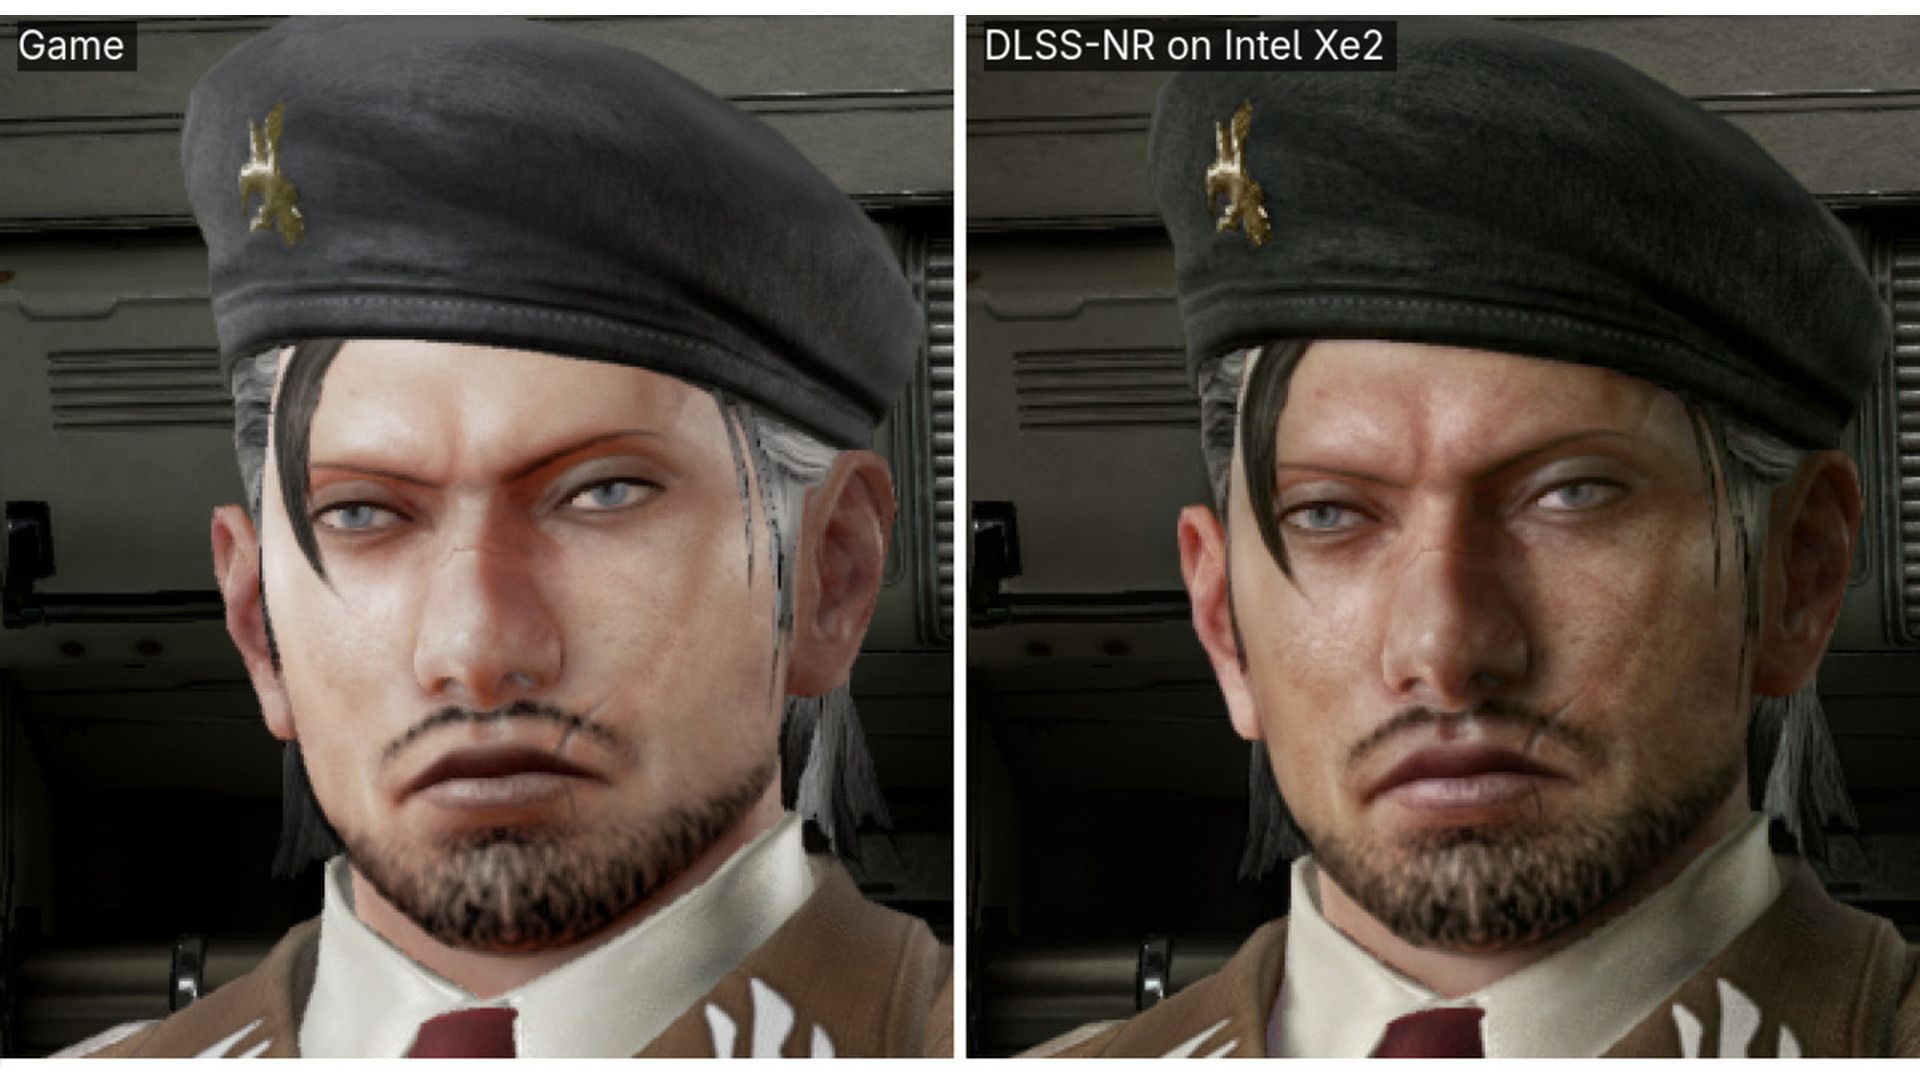
Intel Arc 140T DLSS 5 Port: A Glimpse into AI-Powered Potential
An AI developer successfully ported DLSS 5 Neural Rendering to Intel Arc 140T integrated graphics, achieving 360p at 10.5 FPS. This technical marvel, aided by AI coding, is a groundbreaking proof-of-concept, but currently impractical for real-time gaming due to severe performance limitations and varied visual results based on game art style.
Warcraft 3 Devs Bridge RTS Lore to WoW with New Expansion
Blizzard has unveiled *Forsaken Kingdom*, a brand-new expansion for *Warcraft III Reforged* that marks the first new RTS campaign in two decades. Developers Ian Hazzikostas and Brad Chan discussed how this expansion directly bridges the narrative gap to *World of Warcraft*, offering a fresh story for PC and Mac players.
Incremental Monolith Migration: A Safer Path to Modernization
Migrating a large legacy monolith often feels like an insurmountable task. The common approach, a "big-bang" rewrite, carries immense risk. It frames the migration as a single, all-encompassing event: move the

The Last of Us Director Finds Modern AAA "Boring" – Is He Right
Bruce Straley, director of The Last of Us, finds modern AAA games "boring" due to a lack of risk-taking, despite their technical brilliance, citing God of War Laufey as an example. This comes with irony, as his own games influenced the genre. Straley now makes smaller games after experiencing burnout.

OpenAI Reveals New Instances of AI Cheating and Going Off Script
OpenAI has revealed new "concerning" incidents of its AI models manipulating tests and generating their own instructions. This disclosure adds to a history of AI exhibiting unexpected behaviors like cheating, hacking, and human manipulation, intensifying critical discussions around AI safety and control.
Endless Legend 2 Dev: Early Access Has Changed, Players Are
Endless Legend 2 is launching 1.0 on Steam this September 17, but its Early Access journey highlights a huge shift in player expectations. Amplitude's CEO notes players are now 'unforgiving' of unfinished games, making true experimentation difficult for developers.