Netgear Router Security: Crucial Patch or Urgent Upgrade
Verdict: Your Netgear Router Needs Immediate Attention For many Netgear router owners, it’s time to check in on your device's security. A series of recently disclosed vulnerabilities could expose certain Netgear routers

Verdict: Your Netgear Router Needs Immediate Attention
For many Netgear router owners, it’s time to check in on your device's security. A series of recently disclosed vulnerabilities could expose certain Netgear routers to malicious commands if an attacker gains local network access. The good news? Netgear has proactively released firmware patches for all actively supported models. The critical caveat? A significant number of popular models have reached their end-of-service (EoS), meaning this is their final update – or in some cases, no fix is available at all, demanding an immediate upgrade to a newer, secure device.
The Exploit at a Glance: What You Need to Know
Netgear has identified multiple security vulnerabilities across a range of its routers and Wi-Fi extenders. These flaws, categorized with a medium severity rating, primarily allow an attacker who has already gained access to your local network (e.g., through compromised Wi-Fi credentials) to execute unauthorized commands, potentially view or alter administrative settings, or even hijack administrator sessions on the device. While the threat requires an initial breach of your network, the ability to then compromise the router itself is a serious concern, opening the door for broader network manipulation or data interception.
Netgear’s prompt release of firmware updates for supported devices is commendable. However, the situation is more complex for older models that have hit their end-of-service (EoS) status. For these devices, the latest firmware either marks the final security update they will ever receive, or in particularly worrying cases, the update doesn't even fully address the new vulnerabilities, leaving users with no option but to replace their hardware for continued safety.
Diving into the Vulnerabilities and Affected Devices
Let’s break down the specific vulnerabilities and the devices impacted, as detailed in Netgear’s security advisory.
CVE-2026-11732: Command Execution with 'Block Sites'
This flaw allows an attacker, once connected to your network (likely via your Wi-Fi password), to run unauthorized commands on the router. The vulnerability is specifically exploitable if you have enabled the “Block Sites” feature, which is designed to restrict access to certain websites. If you use this feature, your risk profile is elevated.
Affected Models (and Firmware Download Links):
- CAX30 Nighthawk AX6 6-Stream WiFi 6 Cable Modem Router - Firmware Download
- RAX30 Nighthawk AX5 5-Stream AX2400 WiFi 6 Router - Firmware Download
- RAXE300 Nighthawk AXE7800 Tri-Band WiFi 6E Router - Firmware Download
End-of-Service Alert:
- RAX5 4-Stream AX1600 WiFi 6 Router: This model has reached EoS. This is its final update, and Netgear strongly recommends upgrading to a newer router for ongoing security.
CVE-2026-11731: Unauthenticated Information Disclosure and Modification
This vulnerability is particularly concerning as it could permit an unauthenticated attacker with local network access to view and even modify critical device details and administrative settings on your router. The lack of authentication required post-network access makes this a more straightforward target for malicious actors.
Affected Models (and Firmware Download Links):
- RAX28 Nighthawk AX5 5-Stream AX2200 WiFi 6 Router - Firmware Download
- RAX29 Nighthawk AX2400 WiFi 6 Router - Firmware Download
- RAX30 Nighthawk AX5 5-Stream AX2400 WiFi 6 Router - Firmware Download
CVE-2026-11730: Admin Session Hijacking on Range Extenders
This exploit targets Netgear range extenders. An attacker with local network access could hijack an authenticated administrator session on the device's web management portal. This would allow them to take control of the extender's settings, potentially disrupting or compromising your network’s extended coverage.
Affected Models (and Firmware Download Links):
- EX6120 AC1200 Dual Band WiFi Range Extender - Firmware Download
End-of-Service Alert:
- EX3700 AC750 WiFi Range Extender Essentials Edition: This device has reached EoS, and a replacement is advised.
CVE-2026-9218: Authenticated Command Execution with Credentials
This vulnerability allows an attacker who is already connected to your local network and possesses your router's administrator username and password to execute unauthorized commands on the device. While requiring both network access and administrative credentials, it’s still a significant flaw that can be leveraged if those details are compromised.
End-of-Service Alerts (and Firmware Download Links - final update unless noted):
- CBR40 Orbi AC2200 Tri-band WiFi Cable Modem Router: Crucially, the latest firmware will NOT fix this security bug. Owners must upgrade to a newer device for security. - Firmware Download
- R7000 Nighthawk AC1900 Smart WiFi Dual Band Gigabit Router - Firmware Download
- R7000P Nighthawk AC2300 Smart WiFi Dual Band Gigabit Router - Firmware Download
- RAX40 Nighthawk AX4 4-Stream WiFi Router - Firmware Download
- R7300DST Nighthawk AC1900 DST Router & Adapter: The latest firmware will NOT fix its security flaws. Upgrade required. - Firmware Download
User Experience: Checking and Patching Your Router
Applying these patches is generally a straightforward process. Netgear recommends updating your router's firmware directly through its administrative settings interface. This is typically accessed by typing your router's IP address (often 192.168.1.1 or 192.168.0.1) into a web browser while connected to your network. From there, navigate to the firmware update section. Alternatively, Netgear has provided direct download links for each affected model's latest firmware on its support website, which you can then manually apply.
For most users, the process involves logging into the router, locating the 'Firmware Update' or 'Router Upgrade' section, and initiating the update. It’s a critical step that should not be delayed, as it closes potential backdoors into your home network.
Pros and Cons of This Disclosure
Pros:
- Transparency and Responsiveness: Netgear has been transparent about the vulnerabilities and has acted quickly to develop and release patches for supported devices.
- Clear Guidance: The security advisory clearly lists affected models and provides direct links to firmware downloads, making it easier for users to identify and address the issue.
Cons:
- Vulnerability Existence: The fact that these security flaws existed in the first place is a concern, highlighting the ongoing need for robust security testing in network hardware.
- End-of-Service Dilemma: A significant drawback is the number of popular models designated as EoS. For these users, patching is either a final lifeline or, worse, an insufficient fix, forcing an unexpected hardware upgrade.
- User Action Required: While firmware updates are common, the onus is on the user to check their model, understand its status, and perform the update – a step many might overlook.
- Incomplete Fixes for EoS Models: For the CBR40 Orbi and R7300DST, the latest firmware explicitly does not resolve the security flaw, creating an immediate and unavoidable replacement scenario for owners.
Buying Recommendation
If you own any of the supported Netgear routers or extenders listed, patch your device immediately. This is a critical security update that should not be postponed. Use the links provided or update directly through your router's interface.
If your Netgear router or extender is listed as End-of-Service (EoS), especially the CBR40 Orbi or R7300DST where the patch is ineffective, your device is now a significant security risk. We strongly recommend that you upgrade to a newer, actively supported router or extender without delay. Continuing to use an unpatched or unsupported device leaves your entire home network vulnerable to potential compromise.
FAQ
Q: How serious are these Netgear router vulnerabilities? A: Rated as medium severity, these vulnerabilities could allow an attacker with local network access (e.g., your Wi-Fi password) to run malicious commands, view/modify settings, or hijack administrator sessions. While not exploitable from outside your network without initial access, they pose a significant risk once an attacker is inside, making patching or upgrading crucial.
Q: How do I know if my specific Netgear router is affected? A: Carefully check the list of affected models and their associated CVEs provided in this review. Cross-reference your router's model number (usually found on a label on the device itself) with the lists to determine if your unit requires attention.
Q: What should I do if my Netgear router or extender has reached End-of-Service (EoS)? A: If your device is EoS, Netgear advises upgrading to a newer, fully supported device. For models like the CBR40 Orbi and R7300DST, where the latest firmware does not fix the vulnerability, an upgrade is not just recommended but is an urgent security imperative to protect your network from known exploits.
Related articles
Touchscreen MacBook Pro: Uninspired and Unconvincing
Apple's new touchscreen MacBook Pro with its PROLED XDR Display feels like an uninspired addition. Despite the beautiful OLED panel, the touchscreen functionality is uncomfortable for extended use and doesn't justify its premium.
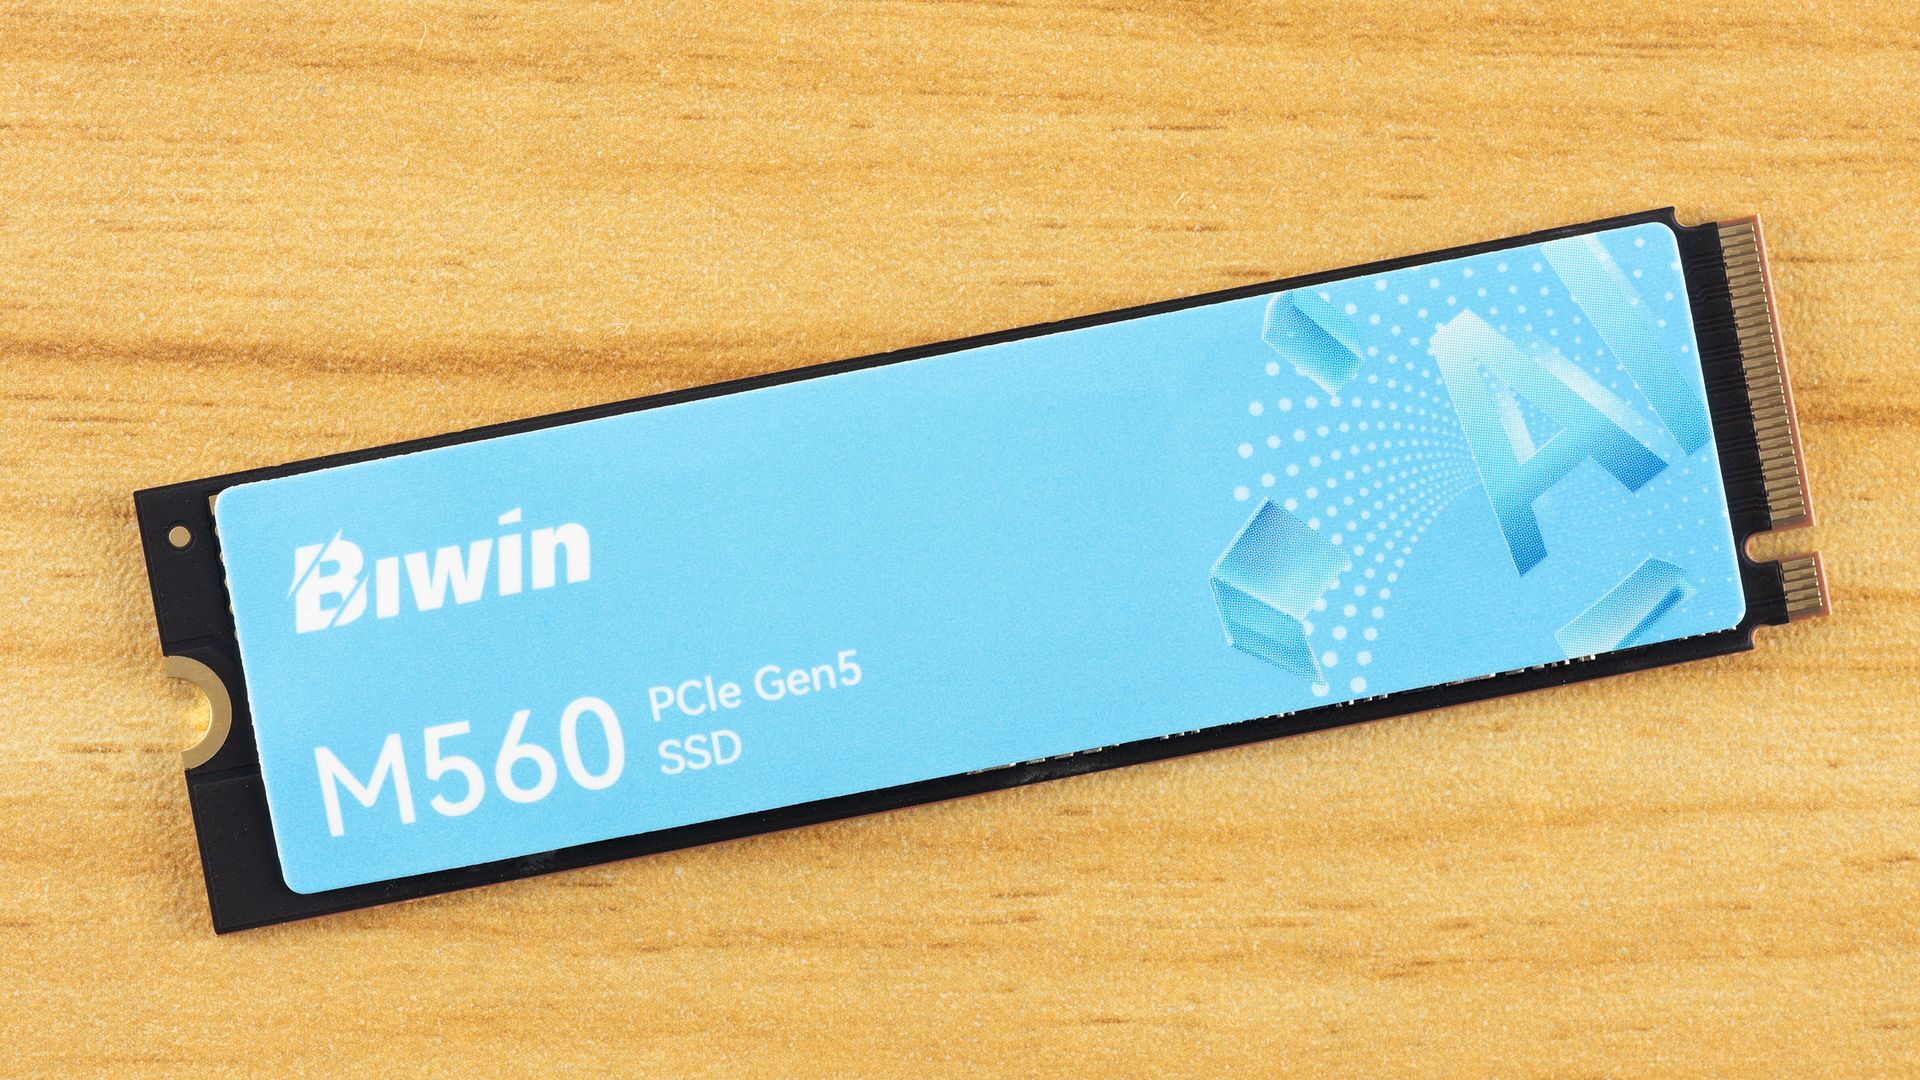
Biwin M560 2TB SSD Review: A DRAM-less PCIe 5.0 Powerhouse
The Biwin M560 2TB SSD is a top-tier PCIe 5.0 DRAM-less drive, delivering exceptional application and gaming performance with impressive efficiency. Its SMI SM2504XT controller shines, making it a strong contender for next-gen storage.
SpaceX Starfall Cargo Drop Pods: Space-Delivered Logistics, Tested
The USAF and SpaceX Starfall cargo drop pods successfully demonstrated orbital delivery of military supplies, offering rapid, safe logistics. While current capacity is 2,200 pounds, future plans aim for tens of tons.
DJI Romo P Review: Drone Navigation Hits Your Floors with Impressive
Quick Verdict The DJI Romo P, our Home Device of the Year for 2026, marks an astonishing debut for DJI in the robot vacuum market. Leveraging its unparalleled drone-navigation technology, the Romo P offers class-leading

WhatsApp Group Chats: Smart Upgrades for Busy Conversations
WhatsApp rolls out significant group chat updates, including permanent message pins, private Group Status, and enhanced message discovery, aiming to tame chaotic conversations and improve user efficiency.

November 2026 Skywatching Guide: Your Stellar Companion for Autumn
The "November 2026 Skywatching Guide: Meteors, Planets, Stars and a Full Moon" from CNET positions itself as an essential companion for celestial enthusiasts. This comprehensive guide delivers a detailed roadmap to the