
Capital One Releases VulnHunter: Open-Source AI for Proactive Security
Capital One has launched VulnHunter, an open-source AI tool designed to identify and fix software vulnerabilities proactively. This agentic AI scans source code using an "attacker-first" approach and a "falsification engine" to minimize false positives, providing targeted code fixes. The move reflects Capital One's commitment to collaborative defense against rising AI threats, especially after its significant 2019 data breach.
Capital One has unveiled VulnHunter, an open-source, agentic AI security tool engineered to proactively discover exploitable vulnerabilities in software. Released Thursday on GitHub under an Apache 2.0 license, VulnHunter scans source code, maps potential attack paths, and proposes targeted fixes—all before the code reaches production environments. This marks a significant move by a major financial institution to transform offensive AI capabilities into a public defensive resource.
Pioneering Proactive AI Defense
VulnHunter introduces an innovative "attacker-first forward analysis" methodology. Instead of traditional scanners that work backward from dangerous code patterns, VulnHunter begins at common entry points like APIs or file uploads, then reasons forward through application logic to confirm if an exploit path exists past existing defenses. This approach dramatically reduces false positives that typically overwhelm engineering teams.
Furthermore, the tool incorporates a unique "falsification engine." After identifying a potential flaw, it rigorously attempts to disprove its own findings, eliminating logical gaps or unsupported assumptions. Only validated vulnerabilities reach human reviewers, complete with a detailed explanation of the exploit path and a proposed code fix, ready for immediate engineering review. The tool currently leverages Anthropic's Claude Opus 4.8 model.
Why Open-Source: A Shared Fight Against Evolving Threats
Capital One's decision to open-source such a critical tool stems from the increasingly interconnected nature of modern software supply chains and the escalating scale of AI threats. Chris Nims, Capital One's CISO, emphasized that securing digital environments is a shared foundation benefiting all developers and enterprises. He noted an "increasingly brief window" before sophisticated AI attack capabilities become widely accessible to adversaries.
Rather than developing a proprietary solution, Capital One opted to build a tool purpose-fit for today’s complex security landscape and distribute it broadly. This strategy aims to allow global security researchers to collectively stress-test, extend, and improve VulnHunter, effectively crowdsourcing the defense infrastructure and strengthening the entire ecosystem.
Rebuilding Trust: Capital One's Post-Breach Commitment
This release arrives in the shadow of the significant 2019 Capital One data breach. The incident, which compromised personal data for approximately 100 million people in the U.S. and 6 million in Canada, including Social Security and bank account numbers, was discovered by an external researcher. The Office of the Comptroller of the Currency subsequently fined Capital One $80 million, citing inadequate risk management and network security controls during its cloud migration.
The breach served as a stark "cautionary tale" for the industry. Capital One's response was not to retreat from technology but to double down, placing security at its core. The company embraced an "open-source first" philosophy in 2015 and joined the Open Source Security Foundation as a premier member in 2022. Its robust Open Source Program Office now manages over 40 projects and thousands of external contributions, making VulnHunter the most impactful outcome of this multi-year commitment.
The VulnHunter Engine: Three Stages of Exploit Discovery
VulnHunter’s advanced architecture operates through three distinct stages. Initially, the attacker-first forward analysis simulates a real adversary’s approach, starting at external interaction points like APIs. It then meticulously traces data flows and internal security checks to confirm if a dangerous code path is genuinely reachable.
The second stage employs the rigorous falsification engine. This component actively attempts to invalidate any identified potential vulnerabilities by searching for logical gaps or conditions preventing an attack. This critical step ensures that developers are presented only with high-fidelity, actionable findings, significantly reducing the noise of false alarms. Finally, for confirmed vulnerabilities, the third stage provides a comprehensive remediation workflow, generating evidence-backed exploit paths, detailed defect explanations, and concrete code changes for immediate review.
Shifting Cyber Paradigms: AI Attacks Demand New Defenses
The urgency behind VulnHunter underscores a fundamental shift in the cybersecurity landscape. Capital One warns that advanced AI models have drastically lowered the barrier for malicious actors to discover and exploit software vulnerabilities at machine speed. Traditional, reactive security measures like patching known flaws are no longer sufficient against these rapidly co-evolving offensive and defensive AI capabilities.
Capital One's own AI security researchers have been at the forefront of tracking these trends, presenting work on LLM safety and adversarial resilience at NeurIPS 2024. VulnHunter's design directly incorporates principles from advanced research, such as multi-agent defense frameworks and automated red-teaming, aiming to counter threats like "jailbreak attacks." The core conviction is that proactive identification and remediation of vulnerabilities are the only sustainable defense in this new era.
A New Baseline for Banking Security?
Capital One's aggressive move into cloud infrastructure, initially complicated by the 2019 breach, has now evolved into a model for pushing security directly into the code. VulnHunter’s open-source release signals a new competitive pressure, potentially establishing a higher standard for enterprise security tooling across financial services and beyond. Its long-term success hinges on broad adoption, active community engagement, and consistent real-world performance against sophisticated AI-powered threats.
FAQ
Q: What makes VulnHunter different from existing vulnerability scanners? A: Unlike conventional scanners that work backward from dangerous code patterns and often produce many false positives, VulnHunter uses an "attacker-first forward analysis." It starts where a real adversary would, tracing attack paths forward, and includes a "falsification engine" that tries to disprove its own findings before they reach a developer, ensuring higher accuracy.
Q: Why did Capital One choose to open-source VulnHunter, rather than keep it proprietary? A: Capital One believes that the scale of modern AI threats and the interconnectedness of software supply chains necessitate a communal defense. By open-sourcing VulnHunter, they aim to enable the global security research community to test, improve, and extend the tool, thereby strengthening the security of the broader ecosystem and their own infrastructure.
Q: How does VulnHunter address the rising threat of AI-powered cyberattacks? A: VulnHunter is specifically designed to combat the new generation of AI threats that lower the barrier for bad actors to find and exploit vulnerabilities at machine speed. By proactively finding and fixing flaws in code before it ships, the tool aims to shift security from a reactive model to a preemptive one, staying ahead of rapidly evolving offensive AI capabilities.
Related articles
TCG Pocket Responds: A Much-Needed Pace Shift for Pokémon Fans
Pokémon TCG Pocket is rolling out a major update for its second anniversary, primarily addressing player concerns about overwhelming content releases by shifting to a six-week set schedule. This aims to curb player decline and improve overall engagement by giving trainers more time to collect and strategize. The update also adds new collection methods, improved deck-building features, and enhanced trading functionality.
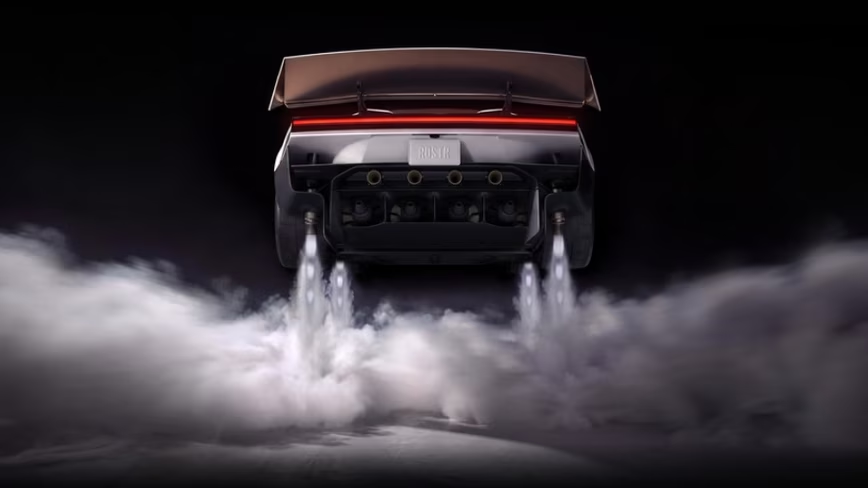
Tesla Unveils Thruster-Equipped Roadster, 2028 Production Targeted
Tesla has unveiled its second-generation Roadster, featuring cold-gas thrusters co-developed with SpaceX, enabling it to jump and flip. The electric sports car demonstrated 0-60mph in an astonishing 0.81 seconds, with production targeted for 2028. This highly anticipated reveal also serves as a key recruitment tool for Tesla's ambitious AI and robotics initiatives.
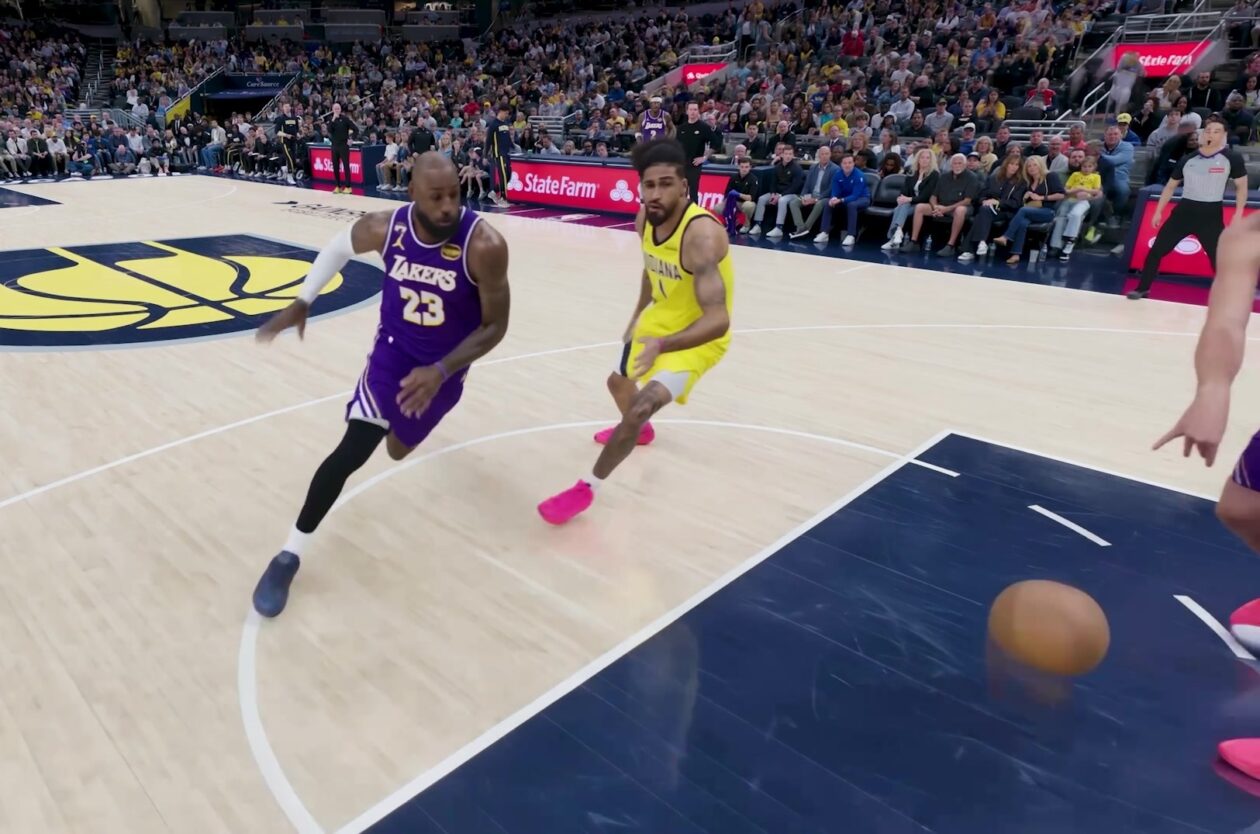
Amazon Prime Video Launches AI-Powered Prime 360 for NBA Coverage
Amazon Prime Video is elevating its NBA coverage with the introduction of Prime 360, an AI-powered replay system offering immersive, 'fly through' views of the action. Kicking off its second season, Prime Video also adds Yahoo fantasy integration and gains exclusive Eastern Conference Finals rights, expanding its tech-driven sports broadcast. The new features aim to deliver a unique and interactive viewing experience for basketball fans.
regional: A two-person Seattle startup lands $1M to reinvent
Seattle startup TriMagnetix has secured $1 million to develop semiconductor chips that consume 800 times less energy and are radiation-resistant. The two-person company, leveraging nanomagnetic technology, is targeting space applications and data centers. With new funding and key partnerships, TriMagnetix aims for commercial sales within a year.
Galaxy Watch One UI 9 Beta: Promising Progress, But Patience Needed
Galaxy Watch 8, Watch Ultra, and Watch 7 are receiving a new One UI 9 Watch beta build with bug fixes and a security patch. Active development signals progress, but a stable release date remains elusive.

in-depth: The Best Permanent Outdoor Lights (2026): Govee, Eufy
WIRED, a leading voice in technology journalism, has just released its updated guide for 2026 on the best permanent outdoor lights, spotlighting top contenders Govee, Eufy, and Cync. These innovative eave lights are